D[AI]NGEN Desktop — Packaged release launched October 21, 2026 · Available for qualified deploymentsRequest Installation →

INVESTORS

A new security boundary for enterprise AI.

AI is changing how employees interact with enterprise data. The security problem is not simply whether a user is authorized to access information. It is whether an AI application or agent should inherit that same access. D[AI]NGEN is being built around that distinction.

THE SHIFT

AI creates a new authorization boundary.

Enterprise security systems traditionally make access decisions around users, applications, devices, and services.

AI introduces a different context.

An employee may legitimately access internal files, financial information, customer records, or other enterprise resources. That does not automatically mean every AI application or agent used by that employee should receive the same access.

When user authorization and AI authorization are treated as the same thing, a new security boundary is missing.

D[AI]NGEN is focused on that boundary.

THE PRODUCT THESIS

User access ≠ AI access.

Traditional enterprise security asks whether a user, application, device, or service can access a resource.

AI introduces another question: should the AI workflow receive the same information the user can access?

D[AI]NGEN exists to answer that second question.

THE BOUNDARY MODEL

AI access should be its own security decision.

D[AI]NGEN is built around a simple principle: “AI access is not user access.”

The platform direction is to place a distinct control boundary between enterprise data and AI.

The public D[AI]NGEN security model considers Identity, Data, Destination, and Policy before a security decision is made.

This is the D[AI]NGEN conceptual security model. Individual capabilities are marketed as shipping functionality only after they are verified.

  • Identity
  • Data
  • Destination
  • Policy
Enterprise Data
D[AI]NGEN
Context / Policy
Decision
AI

ALLOW

Conceptually permit the interaction.

REDACT

Conceptually remove sensitive content before proceeding.

DENY

Conceptually prevent the interaction.

PRODUCT VISION

The boundary, in motion.

This 30-second conceptual overview illustrates the access problem D[AI]NGEN is built around.

Conceptual product overview. Individual product capabilities are published only after verification.

D[AI]NGEN security boundary overviewA short conceptual overview of why user access and AI access should be treated as separate decisions.

THE WEDGE

The Browser Extension is the current product surface.

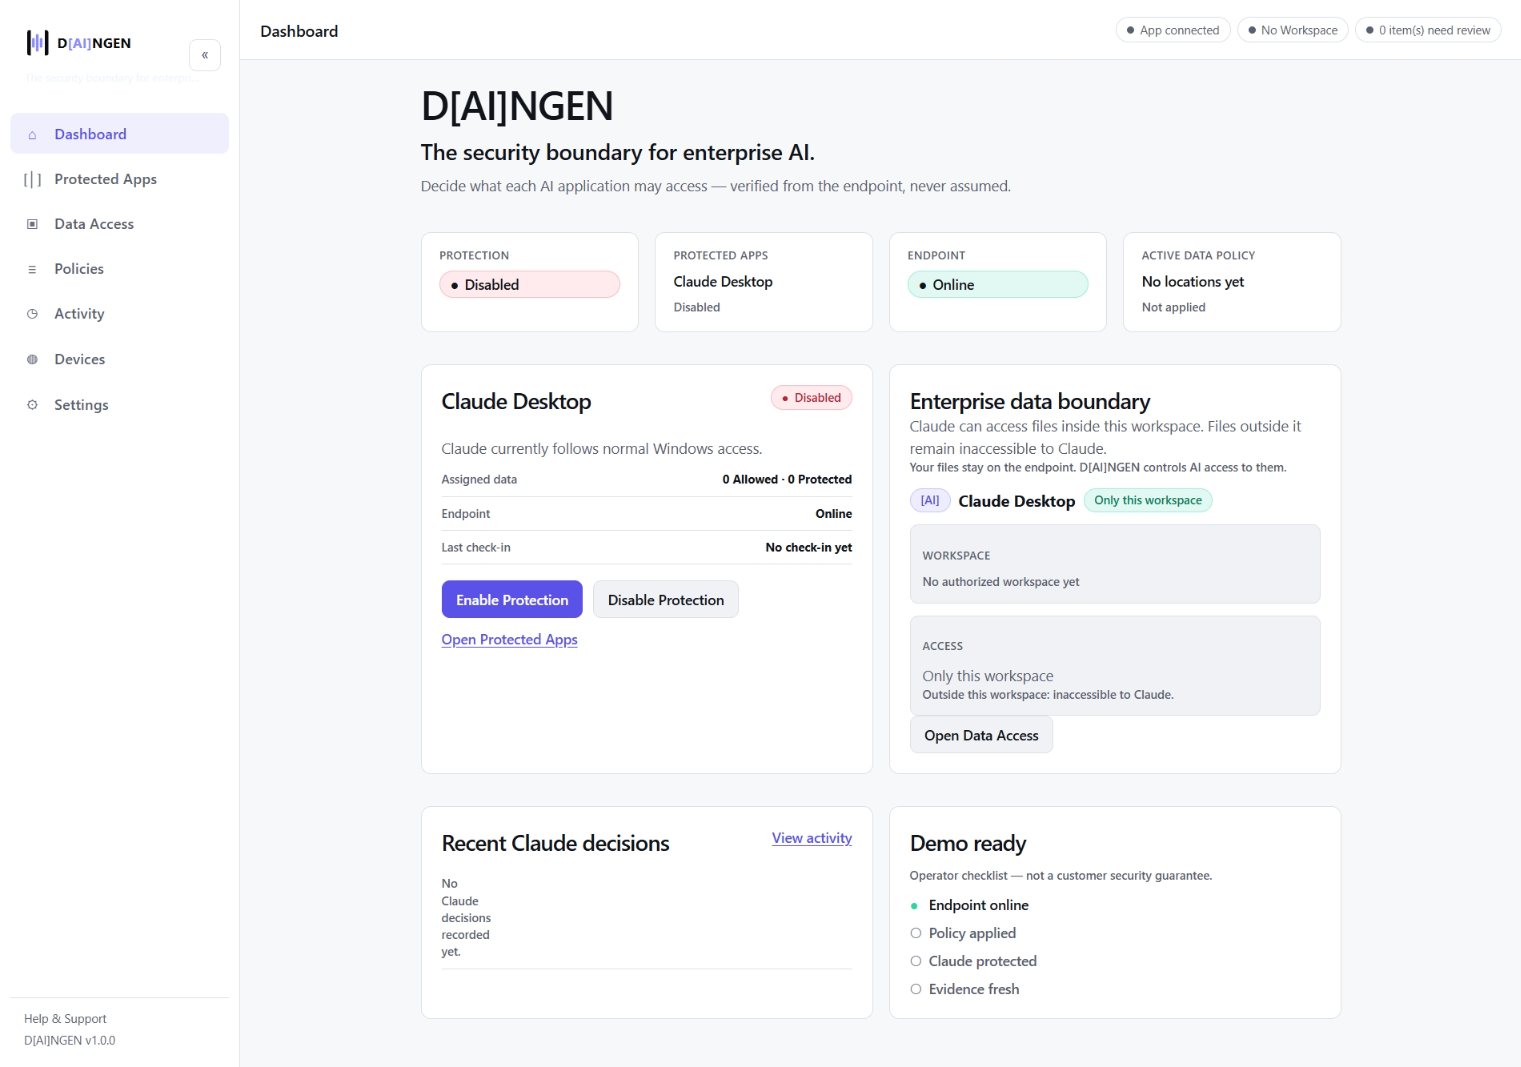
The D[AI]NGEN Browser Extension is the first available product surface and the first concrete expression of the AI-specific access-boundary model.

It brings the product model into browser-based AI workflows while preserving the distinction between what the user may access and what AI should be allowed to access.

D[AI]NGEN Browser Extension dashboard

AVAILABLE NOW · PRIVATE ACCESS

Browser Extension

The current D[AI]NGEN product surface.

THE ENDPOINT CONTROL MODEL

Windows AI-specific access is the core product primitive.

The endpoint model is simple: the employee keeps normal access, while each AI application receives its own independent and more restricted scope.

Approval is scoped to a specific AI application. Claude approved does not mean Gemini approved; Gemini approved does not mean ChatGPT approved.

Finance.xlsx

USERAUTHORIZED
ClaudeAPPROVED
GeminiNOT AUTOMATICALLY APPROVED
ChatGPTNOT AUTOMATICALLY APPROVED

Each AI application receives its own access scope.

PRODUCT MODULE

Discovery & Classification turns scan output into reviewable recommendations.

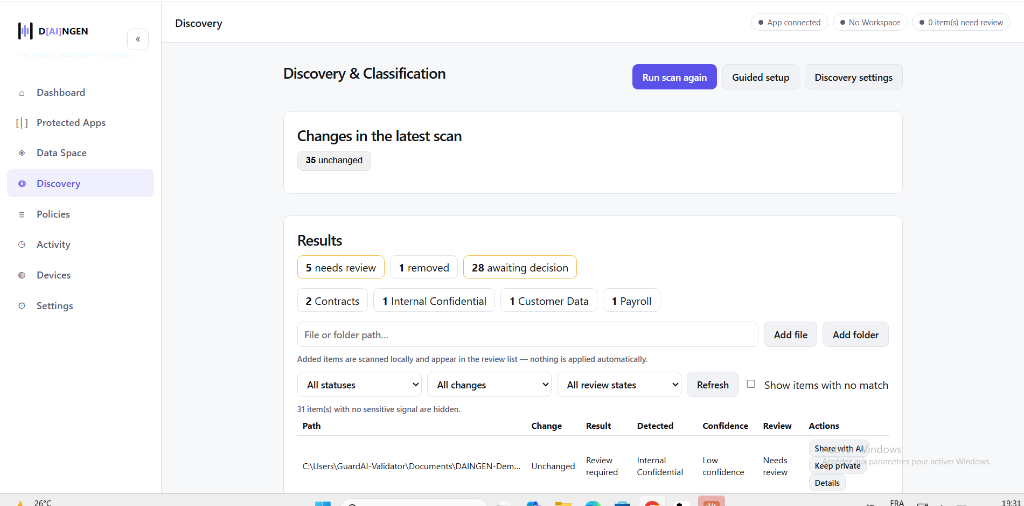
Discovery surfaces AI-relevant files, folders and sensitivity signals locally, then places what needs attention into an admin review flow.

Commercially, this reduces the need to map every resource manually while preserving administrator authority.

Discovery recommends. The admin decides. Nothing is applied automatically.

ADMIN CONTROLS THE SCAN

LOCAL SCAN

Scan and re-scan AI-relevant files and folders inside the governed environment.

RESULTS BY REVIEW STATE

Results group unchanged, removed, needs-review, and awaiting-decision items.

CATEGORIES & SIGNALS

Categories
Sensitivity signals
Awaiting decision

Discovery recommends. The admin decides. Nothing is applied automatically.

D[AI]NGEN Discovery & Classification scan results and review states

Founder-supplied product screenshot showing scan results grouped by review state. The module is recommendation- and review-oriented.

VALIDATED · LIMITED SCOPE

Discovery review workflow

The Discovery & Classification module supports local scan and re-scan workflows, grouped results, categories and sensitivity signals, and administrator review states before policy effect.

Evidence is limited to the visible scan/review workflow. Discovery recommends only; it does not authorize access, create policy autonomously, remediate automatically, or apply enforcement without administrator validation.

PRODUCTIZATION

Deployment relevance

Discovery supports guided setup and administrator review without changing who controls the access decision.

ADMINISTRATION LAYER

The first central-administration foundation is validated.

An initial central-management foundation has been validated: administrative intent can be sent to an enrolled endpoint and applied locally.

The endpoint remains responsible for local filesystem reality and enforcement state. Central administration can receive the metadata and product evidence required for review.

ADMINISTRATIVE INTENT
ENROLLED ENDPOINT
LOCAL ACCESS STATE
PRODUCT EVIDENCE

VALIDATED · LIMITED SCOPE

Initial central-administration foundation

An initial central-management foundation has been validated: administrative intent can be sent to an enrolled endpoint and applied locally.

This is an initial foundation only. It does not establish full multi-device management, group policy at scale, centralized request workflows, or fleet orchestration.

EXECUTION

The product has moved from thesis to validated technical core.

D[AI]NGEN is a validated technical product core moving from functional Alpha/Preview into B2B productization.

This evidence demonstrates product execution and technical maturity within the current evaluated environment. It does not imply general availability or fleet-scale production deployment.

VALIDATED TECHNICAL CORE
B2B PRODUCTIZATION
SCALE

AVAILABLE NOW

Browser

Validated Browser workflows across selected major AI surfaces.

FUNCTIONAL PREVIEW

Windows endpoint

AI-specific Workspace access with the employee retaining normal access.

VALIDATED FOUNDATION

Central administration

Administrative intent can reach an enrolled endpoint and be applied locally.

VALIDATED IN CURRENT EVALUATION

Reliability

Recovery, reset, reboot, Browser/Desktop readiness and protected-session checks have been exercised in the current environment.

PACKAGED RELEASE · OCT 21

Desktop release

The packaged release launched October 21, 2026 for qualified deployments with guided installation. Technical maturity remains Preview.

PRODUCT MODULES / PLATFORM VISION

Access control core. Consumption governance in advanced development.

D[AI]NGEN is presented as a staged enterprise AI control layer: current application/model and data-access control plus Discovery, a launched packaged Desktop release with B2B deployment work, and usage/cost governance in advanced development.

The “how much AI is consumed and at what cost” question now has implemented components in advanced development; live provider integration and end-to-end spending enforcement remain under validation.

CURRENT

CURRENT CORE

  • AI application / model control
  • AI-specific data access
  • Discovery & Classification
  • Local scan / re-scan
  • Review states and sensitivity signals
  • Validated Browser protection
  • Windows Desktop · packaged release (Preview maturity)
  • Protected Workspace model
  • Central administration foundation
  • Endpoint enforcement
  • Decision / evidence foundation
PLANNED

NEXT 90 DAYS

  • Repeatable packaging / deployment
  • Guided installation / pilot onboarding
  • Hardening and pilot readiness
  • Business Profile
  • Privacy preferences
  • Expanded AI app, Workspace, and business-resource inventory
  • Access requests
  • Temporary grants, group policies, and individual exceptions
  • Broader Discovery coverage
  • Broader validated AI coverage
VALIDATION IN PROGRESS

ADVANCED DEVELOPMENT

  • Token measurement from supported provider usage data
  • Per-workstation attribution + calculated costs
  • Budgets, alerts, and spending limits
  • To confirm: live provider integration
  • To confirm: organizational attribution / alert delivery
  • To confirm: end-to-end spending enforcement
  • Later: fleet orchestration / advanced redaction / broader agents

Control what AI can use. Control what AI can access. Control how AI is consumed.

AI usage and cost governance is in advanced development; components are implemented, while live integration and end-to-end enforcement remain under validation.

B2B SCALE PATH

Expand without changing the access model.

The expansion path keeps the same core primitive: AI-specific access boundaries under administrator authority.

V1 can operate endpoint-by-endpoint. Central policy foundation is validated at an initial level; group policy and fleet orchestration remain roadmap.

AVAILABLE

BROWSER EXTENSION

PREVIEW

ENDPOINT BOUNDARY

PRODUCT MODULE

DISCOVERY

VALIDATED FOUNDATION

CENTRAL ADMIN

ROADMAP

B2B SCALE

VALIDATED OVER TIME

MORE AI WORKFLOWS

FROM THESIS TO PRODUCT

The boundary is already running.

The D[AI]NGEN thesis is represented by working product surfaces and narrow validated behavior. This is execution evidence, not a claim that every broad capability category is already verified.

AVAILABLE NOW

Browser

Validated workflows with selected AI services in the current Browser evaluation scope.

FUNCTIONAL PREVIEW

Desktop

Validated Windows Preview with AI-specific Workspace access and scoped endpoint control.

VALIDATED · LIMITED SCOPE

Platform

Scoped decisions, product-state validation, readiness checks, and Alpha RC evidence in evaluated flows.

PRODUCT VALIDATION

Evidence now supports narrower, more concrete product statements.

The current validation layer is intentionally bounded. It describes behavior observed and tested in specific product flows without turning a broad capability category into a generalized guarantee.

For evaluation, this distinction matters: D[AI]NGEN can now discuss concrete browser and Preview behavior while keeping broader capability claims under verification.

VALIDATED · LIMITED SCOPE

Pre-send file review

In covered browser upload flows, a selected file can be held for review before the AI site receives it.

Validation covered selected AI Browser workflows in Chrome. This does not establish coverage for every browser, AI destination, upload path, or file type.

VALIDATED · LIMITED SCOPE

Configured decision outcomes

Configured sensitive-content findings can produce allow, redact, ask-first, or block outcomes in evaluated text and file flows.

This is limited to configured patterns in evaluated flows. It does not establish a complete enterprise policy engine or universal AI policy enforcement.

VALIDATED · LIMITED SCOPE

Discovery review workflow

The Discovery & Classification module supports local scan and re-scan workflows, grouped results, categories and sensitivity signals, and administrator review states before policy effect.

Evidence is limited to the visible scan/review workflow. Discovery recommends only; it does not authorize access, create policy autonomously, remediate automatically, or apply enforcement without administrator validation.

VALIDATED · LIMITED SCOPE

Product-state consistency

The current evaluation validates central and endpoint product-state signals before presenting the environment as ready or protected.

Applies to the evaluated product-state flow only. It does not establish a public SaaS control plane or enterprise-wide management availability.

VALIDATED · LIMITED SCOPE

Readiness and recovery checks

Browser and Desktop readiness, reset, restart, reboot, and protected-session checks have been exercised in the current evaluation environment.

This is scoped reliability evidence for the evaluated environments only. It does not establish enterprise-wide reliability, managed deployment support, or universal compatibility.

VALIDATED · LIMITED SCOPE

Alpha RC validation

The current Alpha RC validation has been completed in the evaluated product environment.

Alpha RC validation is scoped to the evaluated build and does not establish general availability, production readiness, installer availability, or fleet-scale deployment.

VALIDATED · LIMITED SCOPE

Time-limited Workspace grants

The Desktop Preview can make selected local resources available through an authorized Workspace rather than treating the user’s full filesystem access as AI access.

Validated in a Windows alpha environment for selected resources. This does not imply general endpoint isolation, universal filesystem support, or production readiness.

THE EXPANSION

Beyond the browser.

D[AI]NGEN Desktop extends the same security-boundary direction beyond browser-based AI interactions.

D[AI]NGEN Desktop is available today through custom assisted installation for qualified deployments. Its technical maturity remains PREVIEW.

The packaged release launched on October 21, 2026. Self-service distribution and universal fleet-scale readiness are not claimed.

A custom installation does not imply general availability or production readiness at enterprise scale.

Enterprise Resource
D[AI]NGEN Desktop
AI

AVAILABLE NOW · PACKAGED RELEASE

D[AI]NGEN Desktop

Technical maturity: Preview · Packaged release launched: October 21, 2026

EXPANSION LOGIC

Start with the Browser. Extend the boundary.

Browser Extension is the current product surface.

Desktop extends the same AI-specific access model to Windows endpoint workflows.

Discovery and administrator approval reduce deployment friction. The validated central-administration foundation creates the path toward group policy and fleet-scale administration.

Remaining B2B V1 work includes complete onboarding, broader Discovery coverage, richer administrator request workflows, fleet-scale management, and broader validated coverage.

Additional AI workflows can be added as they are validated. This is direction, not a claim that future surfaces or fleet orchestration are already implemented.

BROWSER · AVAILABLE NOW
DESKTOP · PREVIEW
DISCOVERY · PRODUCT MODULE
CENTRAL ADMIN · VALIDATED FOUNDATION
GROUP POLICY · ROADMAP
FLEET ORCHESTRATION · LATER
MORE AI WORKFLOWS

WHY THIS CAN MATTER

The security decision follows AI wherever it enters work.

The underlying problem is not tied to a single AI provider.

It appears whenever a user-authorized environment interacts with an AI workflow.

D[AI]NGEN’s product direction is to apply the same access-boundary principle across additional validated surfaces and workflows.

This expresses product strategy, not current universal coverage.

WHY PRODUCT TRUTH MATTERS

Verification discipline is part of the product.

D[AI]NGEN distinguishes between verified product behavior, preview functionality, conceptual security models, roadmap direction, and capabilities still under validation.

Detailed capabilities are not presented as generally available simply because they appear in architecture discussions, internal builds, demonstrations, or interface screenshots.

For a security product, that discipline is not only a communication policy. It is part of how D[AI]NGEN reduces ambiguity between product direction and verified behavior.

EVIDENCE OF EXECUTION

Execution is separated from ambition.

The public evidence is intentionally scoped: current product, Preview behavior, validated workflows, development targets, and Product Truth remain distinct.

AVAILABLE NOW

Browser

Validated workflows with selected AI services.

FUNCTIONAL PREVIEW

Desktop

Validated Windows Preview with selected-resource Workspace behavior and Alpha RC evidence.

PACKAGED RELEASE · OCT 21

Desktop release

Packaged release available for qualified deployments with guided installation; no self-service or general-availability claim.

4 VALIDATED BROWSER WORKFLOWS

AI Coverage

ChatGPT · Claude · Gemini · Google AI Mode

IN DEVELOPMENT

Roadmap

Cursor · Perplexity · Qwen · Microsoft Copilot · Grok · DeepSeek · Mistral Le Chat

VALIDATION DISCIPLINE

Product Truth

Public claims remain narrower than product ambition.

TEAM

Three co-founders.

The founding team combines CEO, CTO, and COO responsibilities. Biography details are intentionally limited to verified public information.

CO-FOUNDER & CEO

Nadav

Company leadership and investor-facing execution.

CO-FOUNDER & CTO

Yonathan

Technical leadership and product development.

CO-FOUNDER & COO

Mathias

Operations and go-to-market execution.

TRACTION

Early commercial conversations, not customer claims.

Approximately 10 companies are currently in discussion regarding pilot or test deployments.

These discussions are not presented as customers, revenue, production deployment, or completed commercial commitments.

~10 COMPANIES · IN DISCUSSION

Pilot / test discussions

Early evaluation conversations only; no customer, revenue, or signed commitment is claimed.

COMMERCIAL MODEL

Pricing is available on request.

Commercial packaging and indicative pricing assumptions are shared only during qualified evaluation or investor conversations.

No public seat price, package price, annual commitment, or order-form pricing is published at this stage.

ON REQUEST

Pricing

Contact D[AI]NGEN for the current commercial packaging assumptions.

MARKET MODEL

An illustrative bottom-up model, not a third-party market fact.

The investor model currently frames the opportunity as an illustrative bottom-up seat model rather than a validated market study.

It should be read as a commercial hypothesis: addressable enterprise seats multiplied by a private blended-pricing assumption.

ILLUSTRATIVE · $6.0B

TAM

25M addressable enterprise seats under a private blended-pricing assumption.

ILLUSTRATIVE · $1.2B

SAM

5M addressable seats within the modeled enterprise segment.

ILLUSTRATIVE · $12M ANNUAL RECURRING REVENUE

SOM

50,000 seats under the same bottom-up assumptions.

FUNDRAISING

Raising $1M to move from validated core to repeatable B2B deployment.

The intended use of funds is productization and early B2B execution: Windows productization, deployment readiness, security validation, pilot or design-partner deployments, and initial B2B go-to-market.

No valuation, allocation percentage, revenue, or closed-round claim is published.

VALIDATED TECHNICAL CORE
B2B PRODUCTIZATION
PILOT / DESIGN-PARTNER DEPLOYMENTS
INITIAL B2B GO-TO-MARKET

$1M · IN PROGRESS

Current raise

Fundraising language is limited to the current raise and intended use of funds.

Talk to D[AI]NGEN.

For investor conversations, product evaluation, or company inquiries, contact contact@daingen.app.